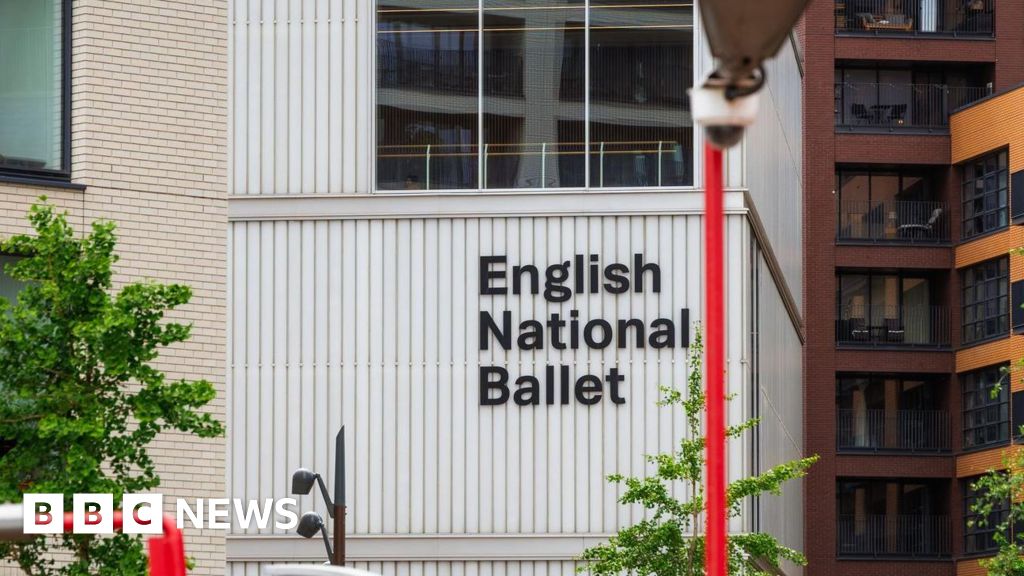
The organisation, which is based in east London, said in an email to those affected that it found out about the hack when it changed its customer relations service and the new provider Beacon CRM “experienced a cybersecurity incident that involved unauthorised access to Beacon’s systems”.